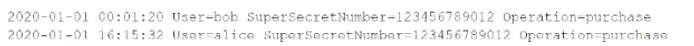Which of the following are valid settings for file and directory monitor inputs?
Correct Answer: B
In Splunk, when configuring file and directory monitor inputs, several settings are available that control how data is indexed and processed. These settings are defined in the inputs.conf file. Among the given options: host: Specifies the hostname associated with the data. It can be set to a static value, or dynamically assigned using settings like host_regex or host_segment. index: Specifies the index where the data will be stored. sourcetype: Defines the data type, which helps Splunk to correctly parse and process the data. TCP_Routing: Used to route data to specific indexers in a distributed environment based on TCP routing rules. host_regex: Allows you to extract the host from the path or filename using a regular expression. host_segment: Identifies the segment of the directory structure (path) to use as the host. Given the options: Option B is correct because it includes host, index, sourcetype, TCP_Routing, host_regex, and host_segment. These are all valid settings for file and directory monitor inputs in Splunk.
Question 52
What is the name of the Splunk index that contains the most valuable information for troubleshooting a Splunk issue?
Correct Answer: B
Question 53
A user has been asked to mask some sensitive data without tampering with the structure of the file /var/log /purchase/transactions. log that has the following format:
Correct Answer: B
Option B is the correct approach because it properly uses a TRANSFORMS stanza in props.conf to reference the transforms.conf for removing sensitive data. The transforms stanza in transforms.conf uses a regular expression (REGEX) to locate the sensitive data (in this case, the SuperSecretNumber) and replaces it with a masked version using the FORMAT directive. In detail: * props.conf refers to the transforms.conf stanza remove_sensitive_data by setting TRANSFORMS- cleanup = remove_sensitive_data. * transforms.conf defines the regular expression that matches the sensitive data and specifies how the sensitive data should be replaced in the FORMAT directive. This approach ensures that sensitive information is masked before indexing without altering the structure of the log files. Splunk Cloud Reference: For further reference, you can look at Splunk's documentation regarding data masking and transformation through props.conf and transforms.conf. Source: * Splunk Docs: Anonymize data * Splunk Docs: Props.conf and Transforms.conf
Question 54
What is the main advantage of managed Splunk Cloud over self-service Splunk Cloud in terms of scalability and reliability?
Correct Answer: C
Question 55
When is data deleted from a Splunk Cloud index?
Correct Answer: A
In Splunk Cloud, data is deleted from an index when the buckets roll to the frozen stage and no archive is defined. When data in a bucket reaches the frozen stage, it is deleted unless a frozen-to-archival script is configured to move the data elsewhere. This process is part of the index lifecycle management in Splunk. Splunk Documentation Reference: Managing Indexes