

Question 26
A rule that detects network connections to an SSH server is triggering constantly in response to background internet traffic and must be tuned. Which method is used to tune this rule and solve the issue?
Question 27
Refer to the exhibit.
An incorrect configuration is shown.
Which setting must you change to successfully apply this configuration to FortiSIEM?
Question 28
Refer to the exhibit.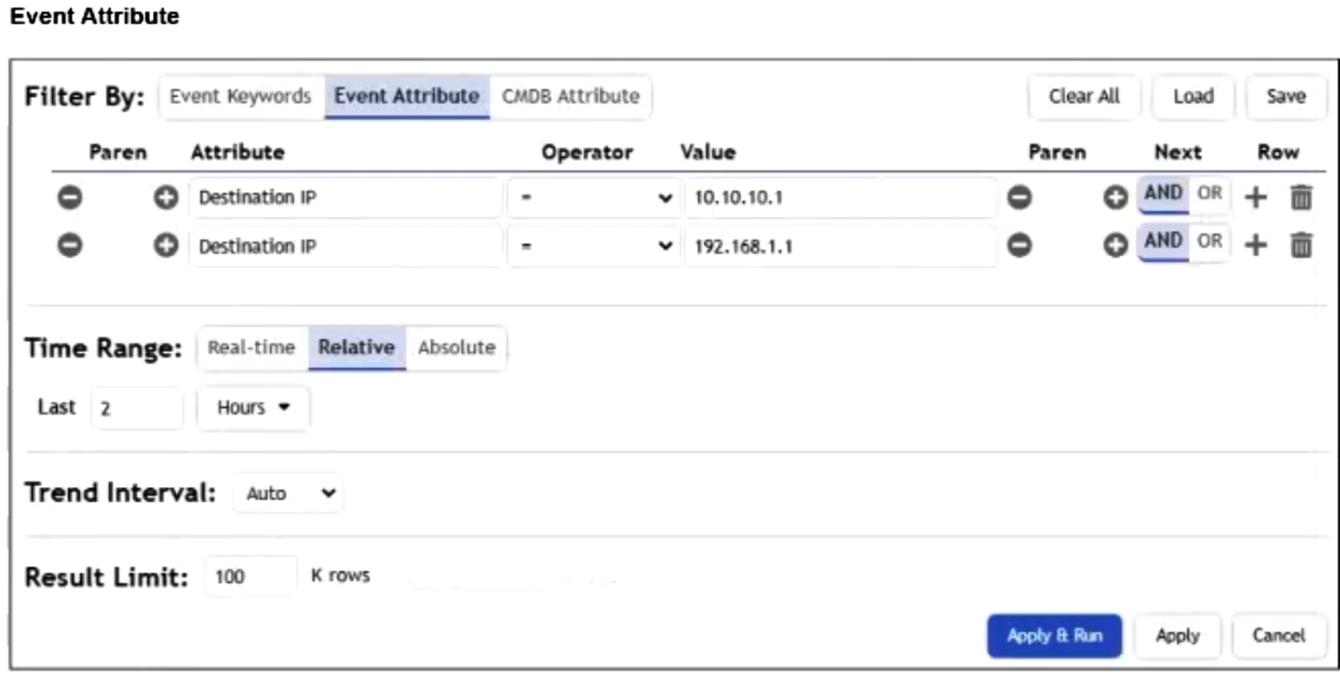
You are investigating an issue with two destination IP addresses, but you are not getting any results from the search.
Based on the filters shown in the exhibit, why is this search returning no results?
Question 29
You need a model that predicts a target field based on other fields in a dataset and then triggers an anomaly if the value does not match the prediction. Which machine learning (ML) algorithm will you use to build this type of model?
Question 30
Which two settings must you configure to allow FortiSIEM to apply tags to devices in FortiClient EMS?
(Choose two.)