Question 31
A security team needs to prevent a remote code execution vulnerability. The vulnerability can be exploited only by sending '${ string in the HTTP request. WAF rule is blocking '${', but system engineers detect that attackers are executing commands on the host anyway. Which action should the security team recommend?
Question 32
An organization fell victim to a ransomware attack that successfully infected 256 hosts within its network. In the aftermath of this incident, the organization's cybersecurity team must prepare a thorough root cause analysis report. This report aims to identify the primary factor or factors that led to the successful ransomware attack and to develop strategies for preventing similar incidents in the future. In this context, what should the cybersecurity engineer include in the root cause analysis report to demonstrate the underlying cause of the incident?
Question 33
Refer to the exhibit.
Question 34
The Linux system administrator of a company suspects that physical unauthorized access was granted to a local Linux terminal. The administrator wants to examine the suspected machine for potential unauthorized use and to get information about even/ account in this terminal including when the password last changed The administrator logs in as a root user Which file should be examined to get the information?
Question 35
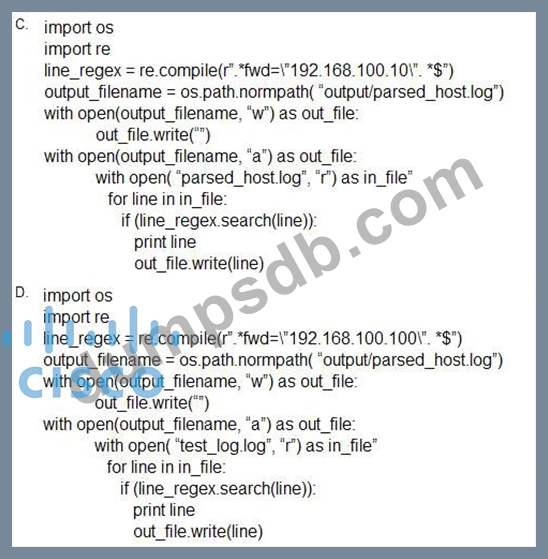
Which scripts will search a log file for the IP address of 192.168.100.100 and create an output file named parsed_host.log while printing results to the console?