

Question 26
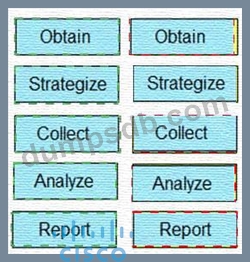
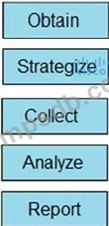
Drag and drop the steps from the left into the order to perform forensics analysis of infrastructure networks on the right.
Question 27
A threat intelligence report identifies an outbreak of a new ransomware strain spreading via phishing emails that contain malicious URLs. A compromised cloud service provider, XYZCloud, is managing the SMTP servers that are sending the phishing emails. A security analyst reviews the potential phishing emails and identifies that the email is coming from XYZCloud. The user has not clicked the embedded malicious URL.
What is the next step that the security analyst should take to identify risk to the organization?
Question 28
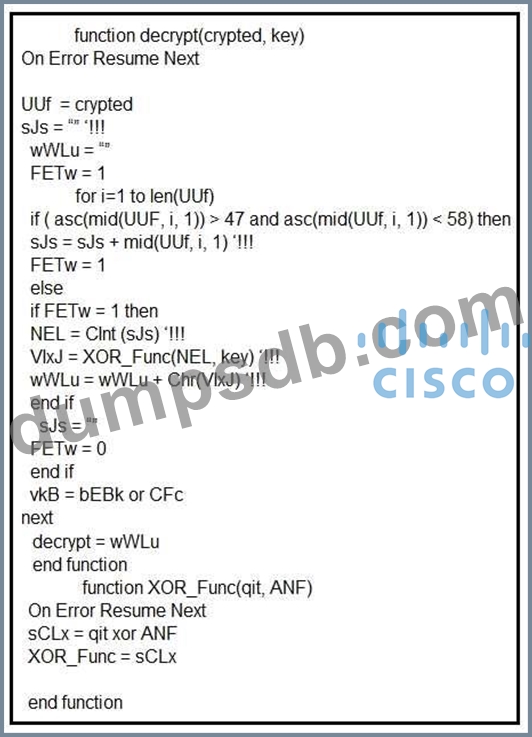
Refer to the exhibit. Which type of code created the snippet?
Question 29
Refer to the exhibit.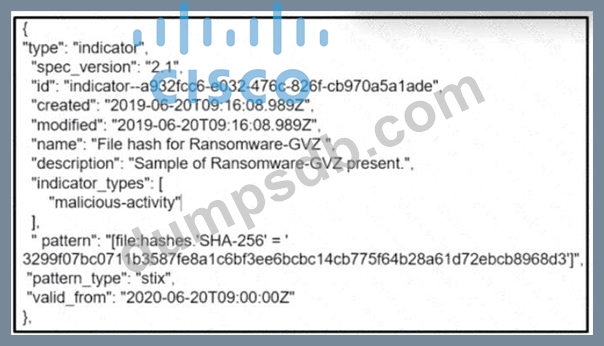
What is the indicator of compromise?
Question 30
An organization publishes a Microsoft Exchange Outlook Web App (OWA) server to provide access to enterprise email and deploys a web application firewall in front of it. Microsoft announces a newly discovered zero-day vulnerability that is being actively exploited. The vulnerability is triggered by a specially crafted request to an uncommonly used URL, and a patch is still being developed. Which action immediately protects the organization?