

Question 6
Over the last year, an organization's HR department has accessed data from its legal department on the last day of each month to create a monthly activity report. An engineer is analyzing suspicious activity alerted by a threat intelligence platform that an authorized user in the HR department has accessed legal data daily for the last week. The engineer pulled the network data from the legal department's shared folders and discovered above average-size data dumps. Which threat actor is implied from these artifacts?
Question 7
Refer to the exhibit.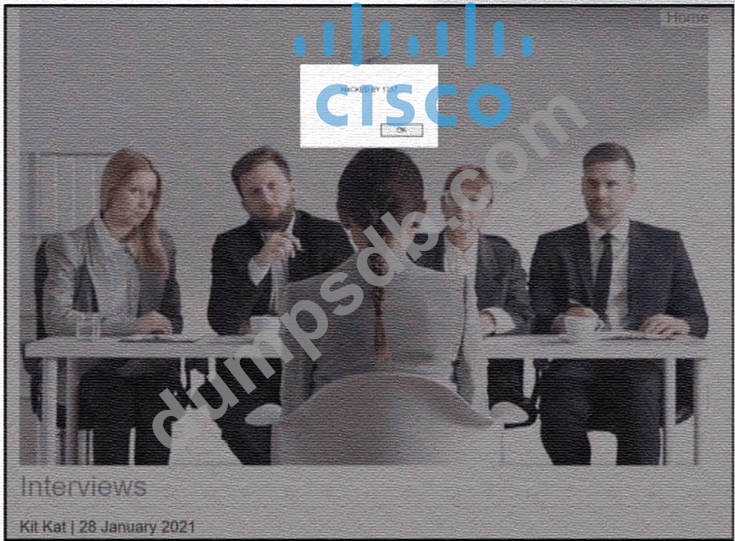
An engineer received a ticket to analyze a recent breach on a company blog. Every time users visit the blog, they are greeted with a message box. The blog allows users to register, log in, create, and provide comments on various topics. Due to the legacy build of the application, it stores user information in the outdated MySQL database. What is the recommended action that an engineer should take?
Question 8
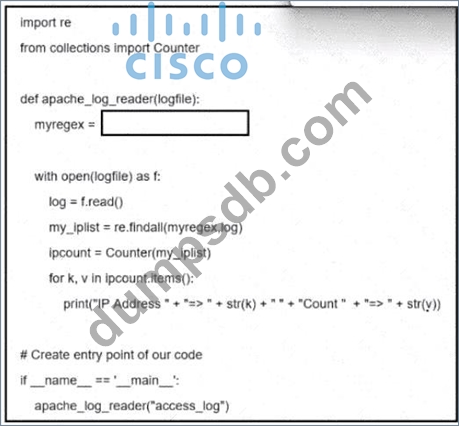
Refer to the exhibit. A network administrator creates an Apache log parser by using Python. What needs to be added in the box where the code is missing to accomplish the requirement?
Question 9
Refer to the exhibit.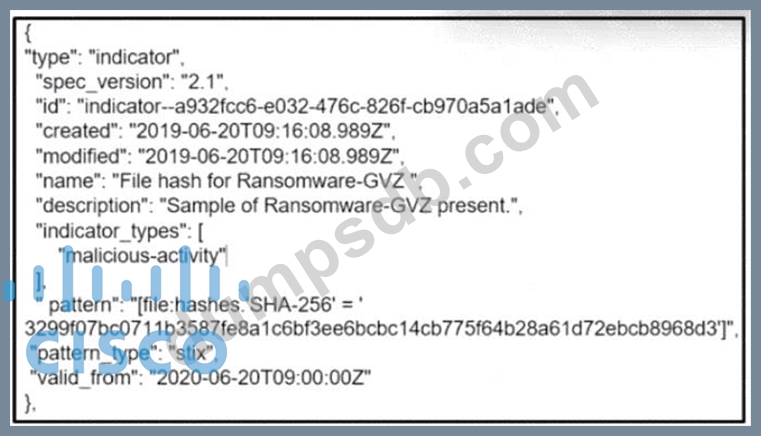
What is the indicator of compromise?
Question 10
A small company must create a temporary detection solution for distributed denial-of-service attacks. An engineer installs Suricata IDPS on an Ubuntu virtual machine and adds a denial-of-service detection rule.
Which rule headers must be used to alert on a SYN-flood attack?