

Question 1
Which antiforensic technique is associated with deliberately misleading forensic analysts by altering the content of digital artifacts, making it difficult to reconstruct the original data accurately?
Question 2
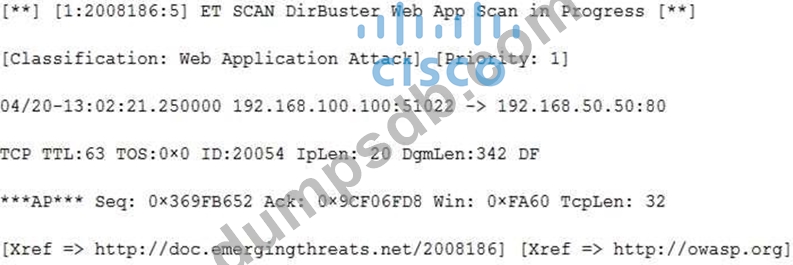
Refer to the exhibit. According to the SNORT alert, what is the attacker performing?
Question 3
Refer to the exhibit.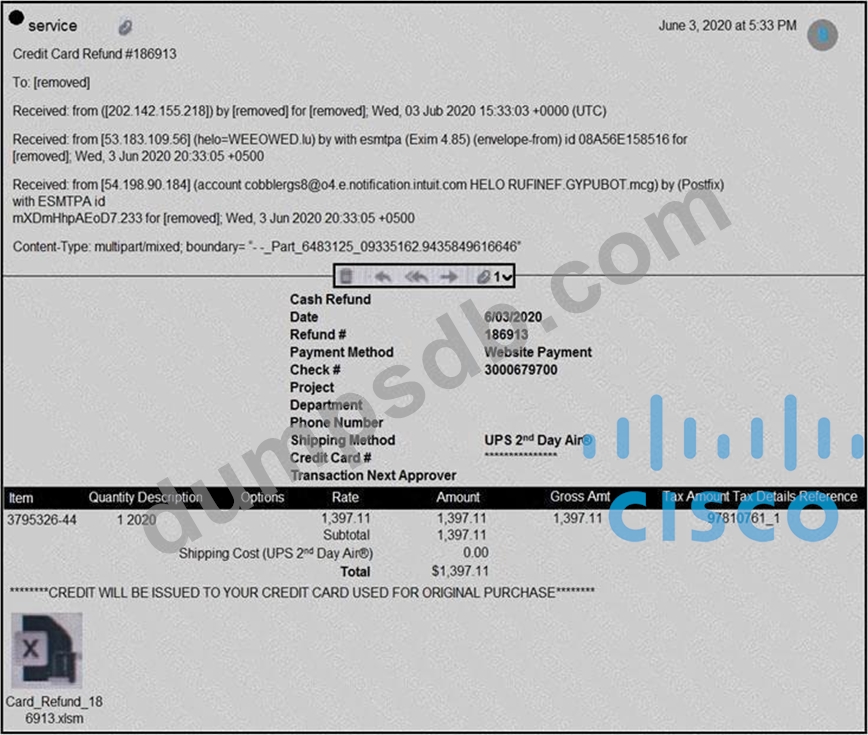
Which element in this email is an indicator of attack?
Question 4
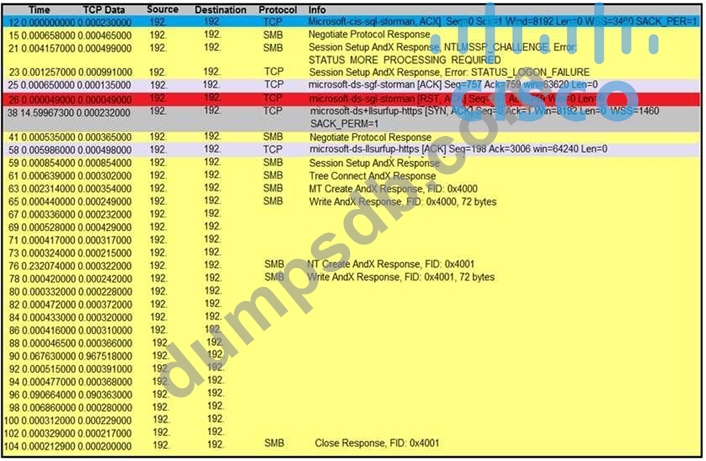
Refer to the exhibit. An engineer is analyzing a TCP stream in a Wireshark after a suspicious email with a URL. What should be determined about the SMB traffic from this stream?
Question 5
Refer to the exhibit.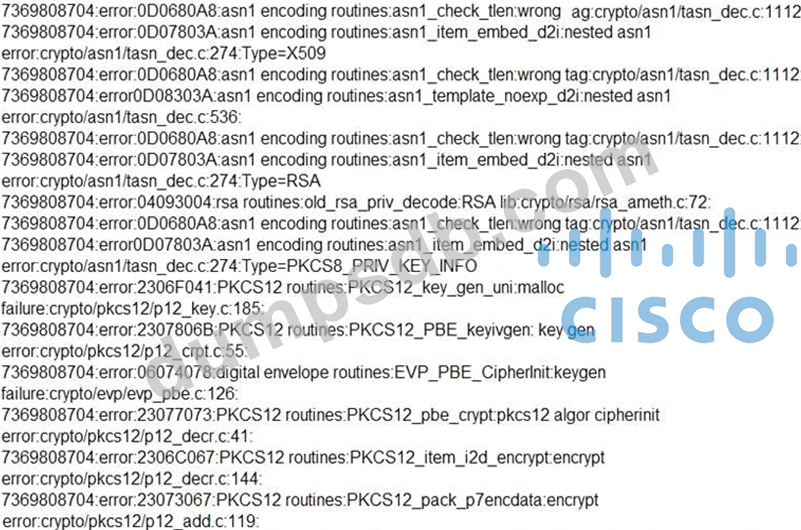
What should be determined from this Apache log?