* C . Collect more evidence on how and when the Human Resources manager pays the ransom fee to unlock personal mobile data, i.e., credit card, and bank transfer. (Relevant to control A.5.26) This is not relevant to the audit of the organization's incident management process. The HR manager's personal phone and how they handle a ransomware attack on it falls outside the scope of the ISMS audit. The organization is not responsible for personal devices. * B . Collect more evidence on how and when the company pays the ransom fee to unlock the company's mobile phone and data, i.e., credit card, and bank transfer. (Relevant to control A.5.26) While seemingly relevant, this focuses on the method of payment for the ransom. The core issue is the organization paying the ransom at all, which is generally not best practice in incident response. The audit should focus on why this decision was made and if alternative solutions were considered (e.g., data backups, device wiping and restoration). Why the other options ARE relevant: * A . Collect more evidence by interviewing more staff about their understanding of the reporting process. (Relevant to control A.6.8) This directly addresses the identified discrepancy in understanding "weakness, event, and incident," which is crucial for proper incident reporting. * D . Collect more evidence on how the organisation determined the incident recovery time. (Relevant to control A.5.27) This investigates the basis for the 24-hour recovery time, which seems arbitrary and may not be appropriate for all incidents. * E . Collect more evidence on how the organization determined no further action was needed after the incident. (Relevant to control A.5.26) This probes the adequacy of the incident response, especially the lack of preventative measures after paying the ransom. * F . Collect more evidence on the incident recovery procedures. (Relevant to control A.5.26) This examines the actual procedures to assess their effectiveness and alignment with best practices.
Comprehensive and Detailed In-Depth Explanation: ISO/IEC 27001 Clause 5.1 (Leadership and Commitment) defines top management's role in ensuring the effectiveness of the Information Security Management System (ISMS). It requires top management to: * Ensure the availability of resources for the ISMS (Correct Responsibility). * Promote continual improvement of the ISMS (Correct Responsibility). * Direct and support employees to contribute to ISMS effectiveness (Correct Responsibility). B). Conducting regular internal audits - Incorrect Responsibility: * Internal audits are not a direct responsibility of top management. Instead, Clause 9.2 (Internal Audit) requires audits to be conducted independently of management. * Top management is responsible for ensuring audits are conducted but does not need to conduct them personally. Thus, top management is responsible for oversight and support but not for conducting internal audits themselves. Relevant Standard Reference: * ISO/IEC 27001:2022 Clause 5.1 (Leadership and Commitment) * ISO/IEC 27001:2022 Clause 9.2 (Internal Audit)
Comprehensive and Detailed In-Depth Explanation: * C. Correct Answer: * ISO/IEC 17021-1:2015 (Requirements for Certification Bodies) prohibits certification bodies from certifying organizations they have provided consultancy services to, unless a two-year separation period is maintained. * This prevents conflicts of interest and ensures independent certification audits. * A. Incorrect: * There is a strict time constraint to prevent certification bias. * B. Incorrect: * Certification cannot happen immediately after consulting services end, as this would create an independence conflict. Relevant Standard Reference: * ISO/IEC 17021-1:2015 Clause 5.2.4 (Impartiality in Certification Activities)
Question 195
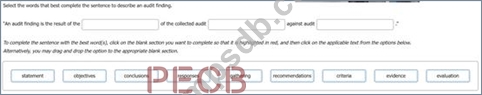
選出最能完整描述審計結果的句子的單字。
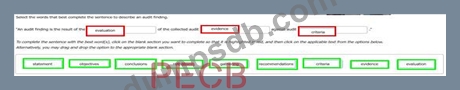
Correct Answer:
Explanation: "An audit finding is the result of the evaluation of the collected audit evidence against audit criteria." The words that best complete the sentence to describe an audit finding are evaluation and evidence. According to ISO 19011:2022, an audit finding is the result of the evaluation of the collected audit evidence against audit criteria12. The other options are either not related to the definition of an audit finding or do not fit the sentence grammatically. References: 1: ISO 19011:2022, Guidelines for auditing management systems, Clause 3.11 \n2: PECB Certified ISO/IEC 27001 Lead Auditor Exam Preparation Guide, Domain 5: Conducting an ISO/IEC 27001 audit